Quick summary
Bug Bounty Hunting training at Best Cybersecurity Training in Hyderabad is a intermediate classroom course in Ameerpet, Hyderabad, in our Offensive Security track. It covers 7 modules — the bounty ecosystem, reconnaissance at scale, content and parameter discovery, high-yield bug classes and more — with hands-on labs using tools such as Burp Suite, ffuf, Amass. It suits learners with web security basics who want to hunt on live programmes.
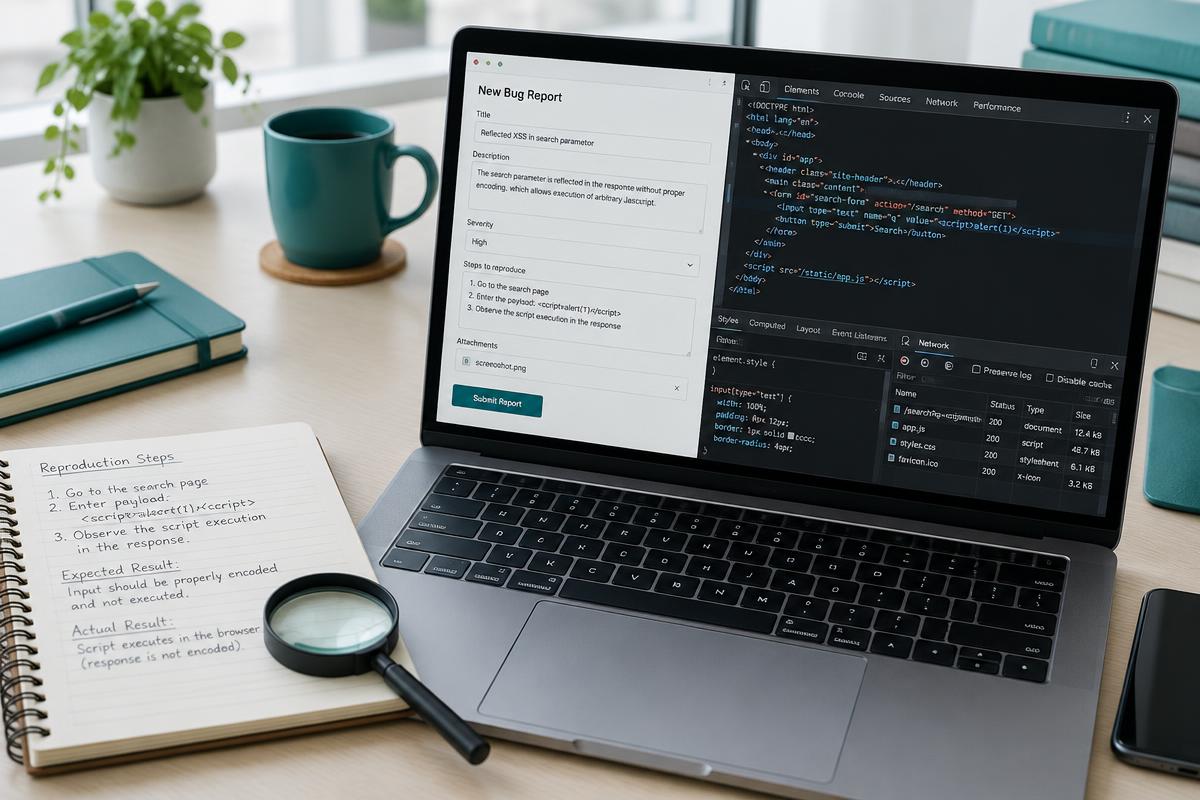
What is the Bug Bounty Hunting course?
Bug bounty hunting rewards method far more than tooling. This course builds a repeatable workflow: choose a programme carefully, map its real attack surface, hunt classes of bugs systematically, and write a report the triage team can validate in minutes.
Substantial time goes to reconnaissance, because that is where most accepted findings originate — forgotten subdomains, stale APIs, unlinked parameters and misconfigured storage. You also learn to read programme policy properly so effort is not wasted on out-of-scope work.
Duplicate and informative outcomes are discussed honestly. Hunting is competitive, and the realistic path is consistent small findings while depth develops.
Who should learn this?
- Learners with web security basics who want to hunt on live programmes
- Ethical hacking students wanting to apply skills legally outside a lab
- Developers with strong application knowledge moving into security research
Prerequisites
- Understanding of HTTP, cookies and sessions
- Prior exposure to common web vulnerability classes
- Comfort with Linux and an intercepting proxy
What you will learn
Bug Bounty Hunting curriculum
M01
The bounty ecosystem
- Public vs private programmes
- Scope, policy and safe harbour
- Severity and reward models
- Duplicate and out-of-scope realities
M02
Reconnaissance at scale
- Subdomain enumeration pipelines
- Certificate transparency and archives
- Port and service discovery
- Technology fingerprinting
M03
Content and parameter discovery
- Directory and file brute forcing
- JavaScript analysis for endpoints
- Hidden parameter discovery
- API route mapping
M04
High-yield bug classes
- Broken access control and IDOR
- Authentication and session flaws
- SSRF
- XSS variants
- Business logic abuse
M05
API and mobile surfaces
- REST and GraphQL testing
- Token handling issues
- Mobile app endpoint extraction
M06
Proof of concept craft
- Minimal reproducible steps
- Impact demonstration without harm
- Evidence capture
- Avoiding destructive testing
M07
Reporting and workflow
- Report structure that triage accepts
- Severity justification
- Handling duplicates and disputes
- Tracking targets over time
Practical training
Practice uses intentionally vulnerable applications plus programmes that publicly permit testing. You build and keep your own recon pipeline and reporting templates.
Tools and technologies
- Burp Suite
- ffuf
- Amass
- Subfinder
- httpx
- nuclei
- Caido or ZAP
- Browser developer tools
Labs and projects
- Build an automated recon pipeline for a single target domain
- Find and chain an IDOR to a meaningful impact in a lab app
- Extract API endpoints from a JavaScript bundle and test them
- Write three complete bounty reports and have them peer-reviewed
Learning outcomes
- Work a target methodically rather than hunting at random
- Produce proof of concept that demonstrates impact safely
- Submit reports that are clear, scoped and reproducible
- Maintain a long-term hunting routine on chosen programmes
Career relevance
Roles where these skills are directly used:
- Bug bounty hunter
- Application security analyst
- Security researcher
- Penetration tester
Bug Bounty Hunting training — FAQs
Can I earn money from bug bounty after this course?
The course gives you the method and the practice. Earnings depend on time invested, target choice and competition — we do not promise income, and anyone who does should be treated with suspicion.
Do I need to know programming?
Reading JavaScript and writing small scripts in Python or Bash is a significant advantage, especially for recon automation. Both are introduced at the level the course needs.
Is testing live websites legal?
Only within the scope and policy of a programme that invites testing. The first module covers scope and safe harbour before any live work.
Should I take web application security first?
If you have not yet studied vulnerability classes in depth, yes — the web application security course covers them systematically and pairs well with this one.
Related cybersecurity courses
Penetration Testing
Technique inside a defensible, repeatable engagement process.
View curriculum
Web Application Security
Every major web vulnerability class, attacked and then fixed.
View curriculum
Mobile Application Security
Test Android and iOS apps the way real assessors do.
View curriculum
API Security
Authorisation, tokens and logic — the three places APIs break.
View curriculum