Quick summary
Threat Hunting training at Best Cybersecurity Training in Hyderabad is a intermediate to advanced classroom course in Ameerpet, Hyderabad, in our Defensive Security track. It covers 8 modules — hunting fundamentals, data readiness, analysis techniques, hunting execution and more — with hands-on labs using tools such as Splunk / Elastic, Sysmon, Velociraptor. It suits sOC analysts at L2 and above.
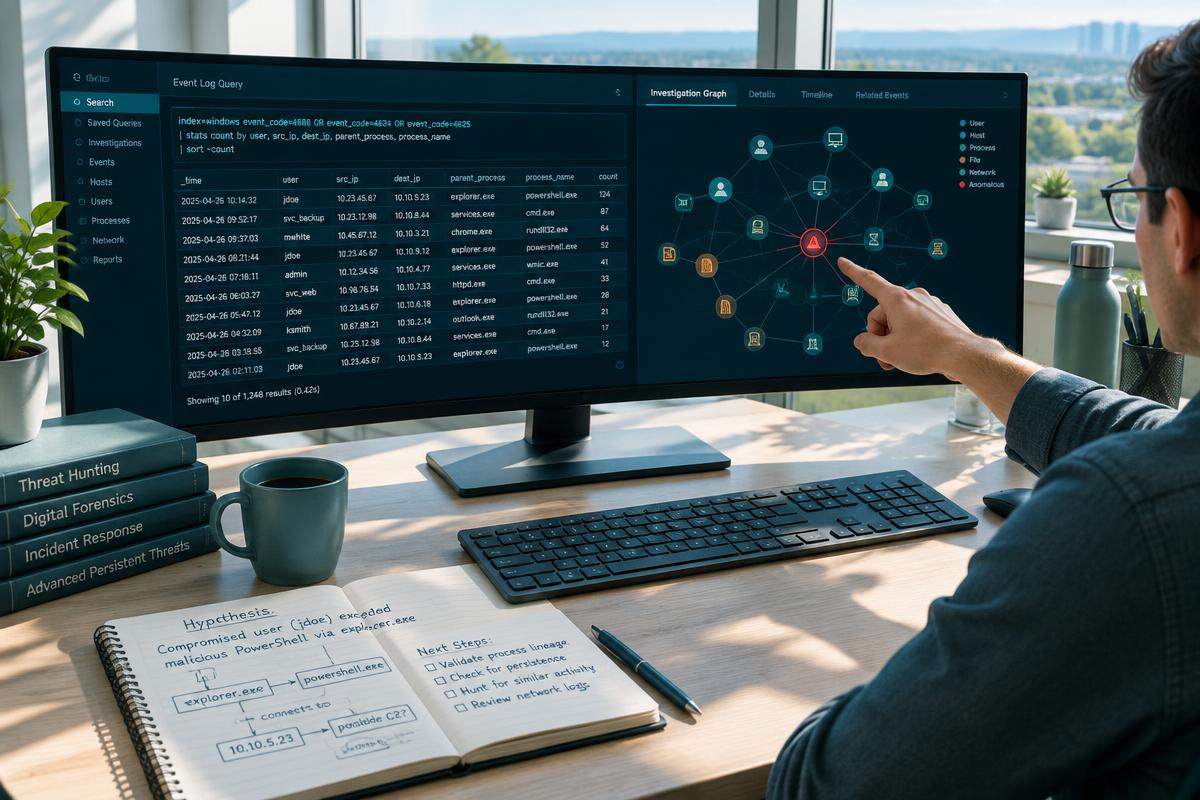
What is the Threat Hunting course?
Threat hunting starts from the assumption that something has already evaded detection. Rather than waiting for an alert, you form a hypothesis about attacker behaviour and test it against your data.
The course teaches hunt structure: hypothesis, data requirements, analysis technique, findings, and the detection or documentation that follows. Every hunt produces an output, even when nothing malicious is found.
Analysis methods include stack counting, frequency analysis, baselining and outlier detection — the techniques that surface quiet activity ordinary alerting misses.
Who should learn this?
- SOC analysts at L2 and above
- Incident responders wanting proactive capability
- Detection engineers validating coverage
- Threat intelligence analysts operationalising reporting
Prerequisites
- Experience investigating alerts in a SIEM or EDR
- Strong Windows internals and networking knowledge
- Familiarity with MITRE ATT&CK
What you will learn
Threat Hunting curriculum
M01
Hunting fundamentals
- Hunting versus alerting
- Hunt maturity models
- Hypothesis sources
- Measuring hunt value
M02
Data readiness
- Required telemetry
- Sysmon and EDR data
- Data quality assessment
- Coverage mapping with ATT&CK
M03
Analysis techniques
- Stack counting and least frequency
- Clustering and grouping
- Baselining
- Visual analysis
M04
Hunting execution
- Suspicious process ancestry
- LOLBin abuse
- Script and PowerShell activity
- Scheduled task and service abuse
M05
Hunting persistence and privilege
- Registry run keys and WMI
- Credential access behaviour
- Token and account anomalies
- Account creation patterns
M06
Hunting network behaviour
- Beaconing detection
- DNS tunnelling
- Rare destination analysis
- Exfiltration signatures
M07
Intelligence-driven hunting
- Using threat reports
- IOC versus TTP hunting
- Adversary emulation input
- Prioritising hunts
M08
From hunt to detection
- Documenting hunts
- Writing new detection rules
- Closing coverage gaps
- Hunt programme reporting
Practical training
You run complete hunts against lab data containing real attack activity, documenting hypothesis, method, result and the detection produced.
Tools and technologies
- Splunk / Elastic
- Sysmon
- Velociraptor
- Zeek
- Jupyter notebooks
- MITRE ATT&CK Navigator
- Sigma
Labs and projects
- Hunt for command-and-control beaconing in network data
- Stack count process execution to find anomalous parent-child pairs
- Hunt WMI and scheduled task persistence across a lab estate
- Convert two hunt findings into tested detection rules
Learning outcomes
- Plan and execute structured hunts independently
- Apply statistical technique to large telemetry sets
- Find activity that existing alerting missed
- Strengthen detection coverage as a routine output of hunting
Career relevance
Roles where these skills are directly used:
- Threat hunter
- Detection engineer
- SOC analyst L3
- Threat intelligence analyst
Threat Hunting training — FAQs
Can a beginner start with threat hunting?
Not realistically. Hunting requires knowing what normal looks like, which comes from investigation experience. Start with the SOC analyst course.
Is an EDR required?
Rich endpoint telemetry is essential. Labs use Sysmon and open tooling to produce equivalent data if you have no commercial EDR.
What if a hunt finds nothing?
That is a normal and useful outcome. It documents coverage and informs the next hypothesis, which is why every hunt must be written up.
Is scripting needed?
Basic Python or query-language fluency helps considerably for large-scale analysis and is introduced where needed.
Related cybersecurity courses
Incident Response
Decide well under pressure, then prove what you did.
View curriculum
Malware Analysis
Determine behaviour, extract indicators, do it safely.
View curriculum
Security Operations Center (SOC)
Work a real alert queue, not a slide deck about one.
View curriculum
Blue Teaming
Build the defences, then prove they detect real technique.
View curriculum