Quick summary
Security Operations Center (SOC) training at Best Cybersecurity Training in Hyderabad is a beginner to intermediate classroom course in Ameerpet, Hyderabad, in our Defensive Security track. It covers 8 modules — soc operations, log sources, siem fundamentals, alert triage and more — with hands-on labs using tools such as Splunk, Elastic Security, Wazuh. It suits graduates and career changers targeting their first security role.
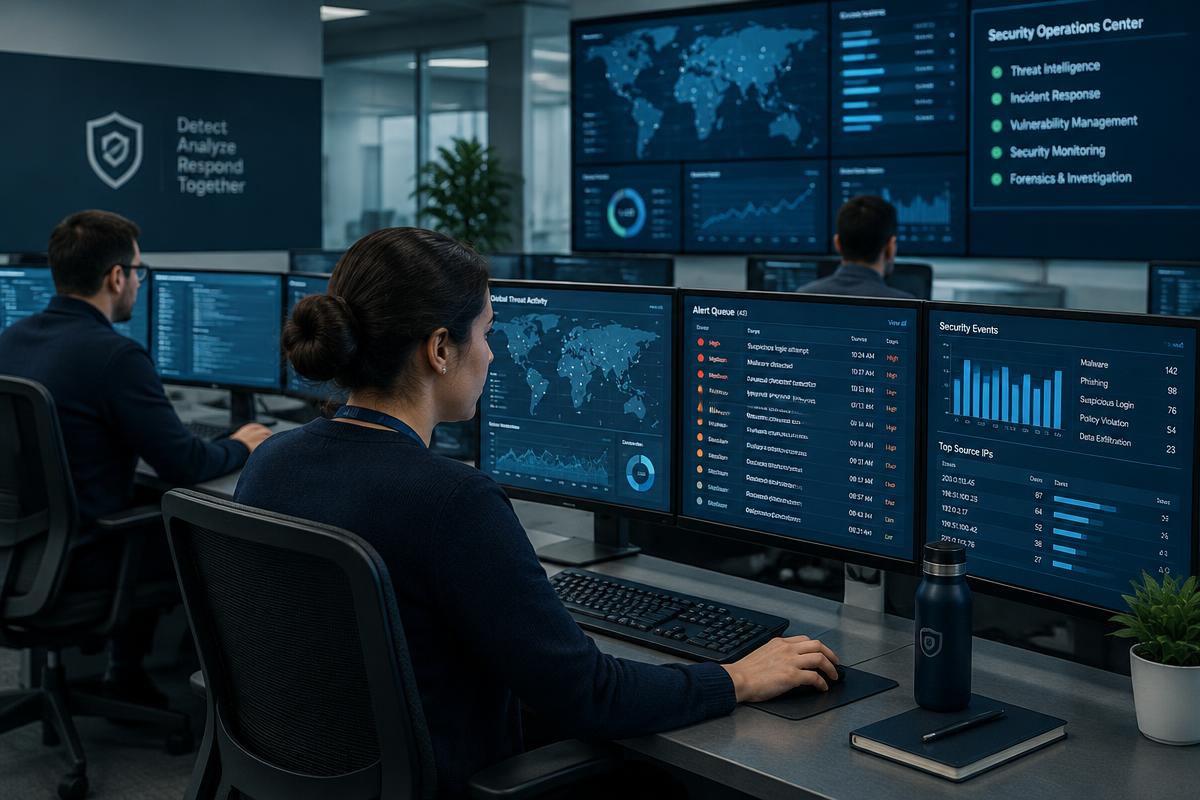
What is the Security Operations Center (SOC) course?
The SOC is where most defensive careers begin. This course prepares you for the actual job: a queue of alerts, incomplete context, and the need to decide quickly whether something matters.
You learn the log sources that carry real signal, how a SIEM correlates them, and how to triage alerts to a consistent standard — including documenting the cases you close as false positives, which is most of them.
Detection engineering is introduced so you can improve the rules that generate your queue instead of only consuming them, which is what distinguishes an L1 who progresses from one who does not.
Who should learn this?
- Graduates and career changers targeting their first security role
- IT support and NOC staff moving into security operations
- Network administrators adding monitoring skills
- Analysts preparing for SOC interviews
Prerequisites
- Networking fundamentals including TCP/IP and DNS
- Windows and Linux basics
- Cybersecurity fundamentals or equivalent
What you will learn
Security Operations Center (SOC) curriculum
M01
SOC operations
- Tiered SOC structure
- Shift handover and case management
- SLAs and metrics
- Analyst workflow discipline
M02
Log sources
- Windows event logs and Sysmon
- Linux auth and audit logs
- Firewall, proxy and DNS logs
- Cloud and identity logs
M03
SIEM fundamentals
- Ingestion and parsing
- Normalisation and enrichment
- Query language practice
- Dashboards and correlation rules
M04
Alert triage
- Validating an alert
- Context gathering checklist
- True versus false positive decisions
- Case documentation standards
M05
Attack recognition
- MITRE ATT&CK in triage
- Phishing indicators
- Credential attacks
- Lateral movement and persistence signals
M06
Investigation practice
- Pivoting across data sources
- Timeline building in the SIEM
- Host and user scoping
- Knowing when to escalate
M07
Detection engineering
- Rule tuning for noise
- Sigma rule writing
- Detection testing
- Coverage gap analysis
M08
Reporting and career readiness
- Case write-ups
- Shift reports
- SOC interview preparation
- Progression from L1 to L2
Practical training
You work a simulated alert queue each session, investigating with a real SIEM against logs generated by live attack activity in the lab.
Tools and technologies
- Splunk
- Elastic Security
- Wazuh
- Sysmon
- Suricata
- MITRE ATT&CK Navigator
- Sigma
Labs and projects
- Investigate a brute force leading to successful authentication
- Trace a phishing-initiated compromise across endpoint and proxy logs
- Tune a high-volume noisy rule without losing true positives
- Write and test Sigma rules for an uncovered technique
Learning outcomes
- Handle an L1 alert queue to a professional standard
- Investigate across multiple log sources confidently
- Escalate with complete, useful context
- Contribute to improving detection coverage
Career relevance
Roles where these skills are directly used:
- SOC analyst L1 and L2
- Security monitoring analyst
- Threat detection analyst
- Incident response analyst
Security Operations Center (SOC) training — FAQs
Is SOC analyst a good first security job?
It is the most common entry point, because it exposes you to the widest range of real attacks early. Shift work is normal and worth considering in advance.
Which SIEM will I learn?
Primarily Splunk and Elastic, with Wazuh in lab builds. The query languages differ, but the investigative method transfers directly.
Do I need prior experience?
Networking and operating system fundamentals are required. If you lack those, take the cybersecurity foundation course first.
Is MITRE ATT&CK covered?
Throughout. It is used as the shared language for describing what an alert represents and for assessing detection coverage.
Related cybersecurity courses
Network Security
Design, defend and monitor the network layer properly.
View curriculum
Incident Response
Decide well under pressure, then prove what you did.
View curriculum
Threat Hunting
Assume the alert never fired. Go and look.
View curriculum
Blue Teaming
Build the defences, then prove they detect real technique.
View curriculum