Quick summary
Web Application Security training at Best Cybersecurity Training in Hyderabad is a intermediate classroom course in Ameerpet, Hyderabad, in our Offensive Security track. It covers 8 modules — web architecture and the attack surface, broken access control, injection, cross-site scripting and more — with hands-on labs using tools such as Burp Suite, OWASP ZAP, SQLMap. It suits web developers responsible for secure delivery.
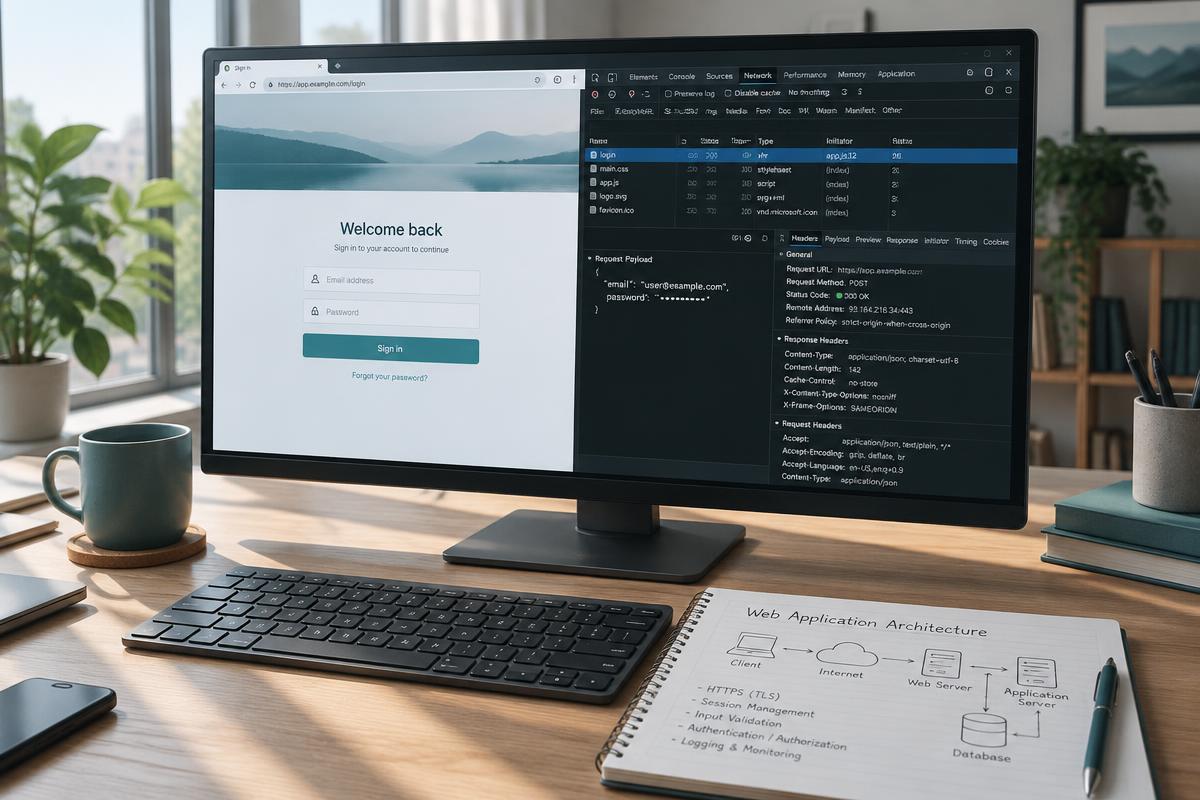
What is the Web Application Security course?
Most breaches that reach the news begin at the web layer. This course works through the vulnerability classes that matter, and for each one you attack a vulnerable implementation and then correct the underlying code or configuration.
The OWASP Top 10 provides structure, but coverage goes beyond the list into logic flaws, modern authentication, and the security implications of single-page applications and third-party components.
Because both attack and fix are covered, the course suits developers and testers equally — and teams benefit when both sides share the same vocabulary.
Who should learn this?
- Web developers responsible for secure delivery
- QA and test engineers adding security testing
- Security analysts specialising in application security
- Bug bounty hunters who want systematic coverage
Prerequisites
- Understanding of HTTP requests, responses and status codes
- Basic HTML, JavaScript and database query familiarity
- Experience using browser developer tools
What you will learn
Web Application Security curriculum
M01
Web architecture and the attack surface
- Request lifecycle
- Same-origin policy and CORS
- Session management models
- Client versus server trust
M02
Broken access control
- IDOR and object-level checks
- Vertical and horizontal escalation
- Forced browsing
- Designing correct authorisation
M03
Injection
- SQL injection variants
- NoSQL and command injection
- Template injection
- Parameterisation and safe APIs
M04
Cross-site scripting
- Reflected, stored and DOM XSS
- Context-aware encoding
- Content Security Policy
- Framework escaping behaviour
M05
Authentication and sessions
- Credential handling and password storage
- MFA weaknesses
- JWT and token pitfalls
- OAuth and OIDC misuse
M06
Server-side flaws
- SSRF
- Insecure deserialisation
- File upload and path traversal
- XXE
M07
Design, configuration and supply chain
- Insecure design patterns
- Security misconfiguration
- Vulnerable dependencies
- Secrets management
M08
Secure development practice
- Threat modelling
- Secure code review
- Security testing in CI
- Developer-facing remediation advice
Practical training
Each class pairs an exploitation lab with a remediation exercise: you break it, then you patch it and prove the fix holds.
Tools and technologies
- Burp Suite
- OWASP ZAP
- SQLMap
- Semgrep
- Docker-based vulnerable apps
- Browser developer tools
Labs and projects
- Exploit and then fix a SQL injection in an application you are given source for
- Bypass an access control model, then redesign it correctly
- Build a working CSP for a vulnerable single-page application
- Conduct a secure code review and report findings to a developer audience
Learning outcomes
- Test a web application systematically against a defined checklist
- Explain vulnerabilities in terms developers can act on
- Implement framework-level defences correctly
- Support secure development rather than only reporting problems
Career relevance
Roles where these skills are directly used:
- Application security engineer
- Penetration tester (web)
- Secure code reviewer
- Security-focused developer
Web Application Security training — FAQs
Is this course for developers or for testers?
Both. Attack labs matter to testers and fix labs matter to developers, and each group benefits from seeing the other half of the problem.
Do you cover API and GraphQL security?
At an introductory level here. The dedicated API security course goes considerably deeper into authorisation, rate limiting and GraphQL-specific issues.
Which programming language is used?
Lab applications span common stacks. The principles are language-independent, and remediation is shown in the framework idiom where it matters.
Does this help with bug bounty hunting?
Substantially. Most accepted bounty findings fall into the classes covered here, which is why many hunters take this course first.
Related cybersecurity courses
Bug Bounty Hunting
Recon depth, repeatable method and reports that get accepted.
View curriculum
Penetration Testing
Technique inside a defensible, repeatable engagement process.
View curriculum
Mobile Application Security
Test Android and iOS apps the way real assessors do.
View curriculum
API Security
Authorisation, tokens and logic — the three places APIs break.
View curriculum