Quick summary
Wireless Network Security training at Best Cybersecurity Training in Hyderabad is a intermediate classroom course in Ameerpet, Hyderabad, in our Infrastructure Security track. It covers 8 modules — wireless fundamentals, wireless security evolution, attacks on personal networks, rogue infrastructure and more — with hands-on labs using tools such as Aircrack-ng suite, hcxdumptool, hashcat. It suits network engineers managing wireless infrastructure.
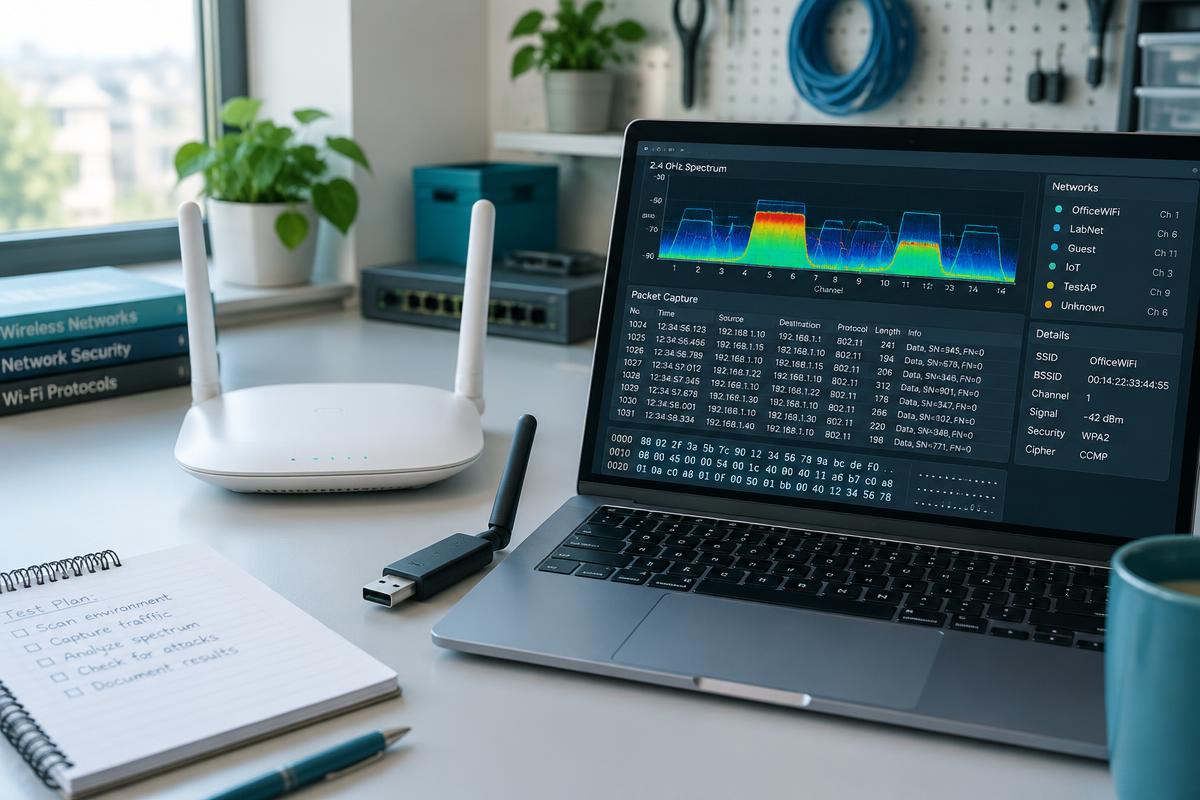
What is the Wireless Network Security course?
Wireless extends a network beyond physical control, and it is frequently the weakest documented part of an estate. This course covers how Wi-Fi security actually works and where it fails.
You study 802.11 at frame level, the evolution from WEP through WPA3, and the authentication models used in enterprise deployments, then attack each in a controlled lab environment.
Defence receives equal attention: enterprise authentication design, segmentation for wireless clients, rogue access point detection and monitoring.
Who should learn this?
- Network engineers managing wireless infrastructure
- Penetration testers adding wireless to their scope
- Security analysts assessing office environments
- IT staff deploying enterprise Wi-Fi
Prerequisites
- Networking fundamentals
- Linux command line comfort
- A compatible wireless adapter is recommended for full lab participation
What you will learn
Wireless Network Security curriculum
M01
Wireless fundamentals
- 802.11 standards and bands
- Frame types and management frames
- Monitor mode and capture
- RF behaviour basics
M02
Wireless security evolution
- WEP and why it failed
- WPA and WPA2
- WPA3 and SAE
- Transition mode weaknesses
M03
Attacks on personal networks
- Handshake capture
- Offline cracking
- PMKID attacks
- Deauthentication effects
M04
Rogue infrastructure
- Evil twin access points
- Captive portal attacks
- Client probe exploitation
- Detection of rogue devices
M05
Enterprise wireless
- 802.1X and RADIUS
- EAP method comparison
- Certificate validation failures
- Credential theft scenarios
M06
Other wireless surfaces
- Bluetooth risk overview
- IoT wireless protocols
- Guest network design
- BYOD considerations
M07
Defence and monitoring
- Wireless segmentation
- WIDS/WIPS concepts
- Configuration hardening
- Site survey for security
M08
Assessment practice
- Wireless assessment methodology
- Evidence and physical context
- Reporting
- Remediation guidance
Practical training
Labs run against access points we control in an isolated RF environment, covering both attack execution and the detection each attack generates.
Tools and technologies
- Aircrack-ng suite
- hcxdumptool
- hashcat
- Wireshark
- Kismet
- hostapd
- FreeRADIUS
Labs and projects
- Capture a WPA2 handshake and assess passphrase strength offline
- Stand up and then detect an evil twin access point
- Test an enterprise 802.1X deployment for certificate validation weaknesses
- Design and document a segmented corporate wireless architecture
Learning outcomes
- Assess a wireless deployment methodically
- Explain WPA2 and WPA3 weaknesses accurately
- Design wireless networks that limit the blast radius of compromise
- Detect rogue wireless activity in an environment
Career relevance
Roles where these skills are directly used:
- Wireless security engineer
- Network security engineer
- Penetration tester
- Infrastructure security analyst
Wireless Network Security training — FAQs
Do I need special hardware?
A wireless adapter supporting monitor mode and packet injection is needed for full participation. We advise on suitable models before the course starts.
Is WPA3 secure?
It is a significant improvement, particularly against offline cracking, but transition modes and implementation flaws still create exposure — both are covered.
Can I test my office Wi-Fi?
Only with written authorisation from whoever owns it. Testing without permission is unlawful, and the course covers authorisation before any attack content.
Is Bluetooth and IoT included?
At overview level, enough to assess risk and know when specialist testing is needed.
Related cybersecurity courses
Penetration Testing
Technique inside a defensible, repeatable engagement process.
View curriculum
Network Security
Design, defend and monitor the network layer properly.
View curriculum
Vulnerability Assessment
Scanning is easy. Prioritising and closing findings is the job.
View curriculum
Cryptography
Applied, not academic — the mistakes that actually break systems.
View curriculum