Quick summary
Ethical Hacking training at Best Cybersecurity Training in Hyderabad is a beginner to intermediate classroom course in Ameerpet, Hyderabad, in our Offensive Security track. It covers 8 modules — legal and ethical framework, reconnaissance, scanning and enumeration, system hacking and more — with hands-on labs using tools such as Kali Linux, Nmap, Metasploit Framework. It suits learners with cybersecurity fundamentals who want offensive skills.
What is the Ethical Hacking course?
Ethical hacking is the disciplined practice of attacking systems you have written permission to attack, then explaining precisely what you did and how to prevent it. This course teaches the full sequence rather than isolated tricks.
You work through reconnaissance, enumeration, exploitation, privilege escalation and post-exploitation against deliberately vulnerable targets in a closed lab. Tooling is taught alongside the underlying mechanism, so you understand why an exploit lands rather than which button produced it.
Reporting is treated as a core skill. A finding nobody can act on has no value, so you write up every engagement exercise with evidence, impact and remediation.
Who should learn this?
- Learners with cybersecurity fundamentals who want offensive skills
- System and network administrators who want to test their own infrastructure
- Developers who want to understand how their applications get broken
- Candidates preparing for offensive-security certification study
Prerequisites
- Working knowledge of TCP/IP and DNS
- Comfort with the Linux command line
- Basic understanding of how web applications work
What you will learn
Ethical Hacking curriculum
M01
Legal and ethical framework
- Authorisation and scope documents
- Rules of engagement
- Indian legal context for security testing
- Responsible disclosure
M02
Reconnaissance
- OSINT sources and techniques
- DNS and subdomain discovery
- Metadata and exposure review
- Attack surface mapping
M03
Scanning and enumeration
- Nmap scanning strategy
- Service and version fingerprinting
- SMB, SNMP and LDAP enumeration
- Vulnerability scanner interpretation
M04
System hacking
- Password attacks and cracking
- Exploiting unpatched services
- Metasploit workflow
- Payloads and shells
M05
Privilege escalation
- Linux escalation paths
- Windows escalation paths
- Token and service abuse
- Escalation enumeration scripts
M06
Web application attacks
- Injection flaws
- Broken authentication
- Access control testing
- File upload and inclusion issues
M07
Network attacks
- Sniffing and spoofing
- Man-in-the-middle scenarios
- Pivoting between networks
- Wireless attack overview
M08
Post-exploitation and reporting
- Persistence concepts
- Evidence collection
- Cleanup responsibilities
- Writing the engagement report
Practical training
The course runs on an isolated lab network of intentionally vulnerable machines. Each attack chain is executed by you, not demonstrated at you, and every exercise ends with a short written finding.
Tools and technologies
- Kali Linux
- Nmap
- Metasploit Framework
- Burp Suite
- Hydra
- John the Ripper
- Hashcat
- Wireshark
- Gobuster
Labs and projects
- Full compromise of a vulnerable Linux host from scan to root
- Active Directory style enumeration and lateral movement in a lab domain
- Web application exploitation chain ending in server access
- Produce a complete assessment report for one lab environment
Learning outcomes
- Run an authorised assessment against a small environment unaided
- Select and justify technique instead of running tools blindly
- Document findings to a standard a client or employer can act on
- Move on to penetration testing, red teaming or bug bounty work
Career relevance
Roles where these skills are directly used:
- Ethical hacker
- Junior penetration tester
- Security analyst
- Vulnerability assessment engineer
Ethical Hacking training — FAQs
Is ethical hacking legal in India?
Testing a system you have written authorisation to test is legal. Testing without that permission is an offence under the Information Technology Act. The course starts with scope and authorisation for exactly this reason.
Do I need programming for ethical hacking?
Not to begin. You will read and adapt scripts, and basic Python or Bash makes you considerably faster, so scripting is introduced where it is needed.
How is this different from your penetration testing course?
Ethical hacking teaches technique. Penetration testing teaches the professional engagement around that technique — methodology, scoping, structured reporting and client delivery.
Will I practise on real websites?
No. All practice happens against lab targets we provide or public platforms that explicitly permit testing. Unauthorised testing is never part of the course.
Related cybersecurity courses
Bug Bounty Hunting
Recon depth, repeatable method and reports that get accepted.
View curriculum
Penetration Testing
Technique inside a defensible, repeatable engagement process.
View curriculum
Web Application Security
Every major web vulnerability class, attacked and then fixed.
View curriculum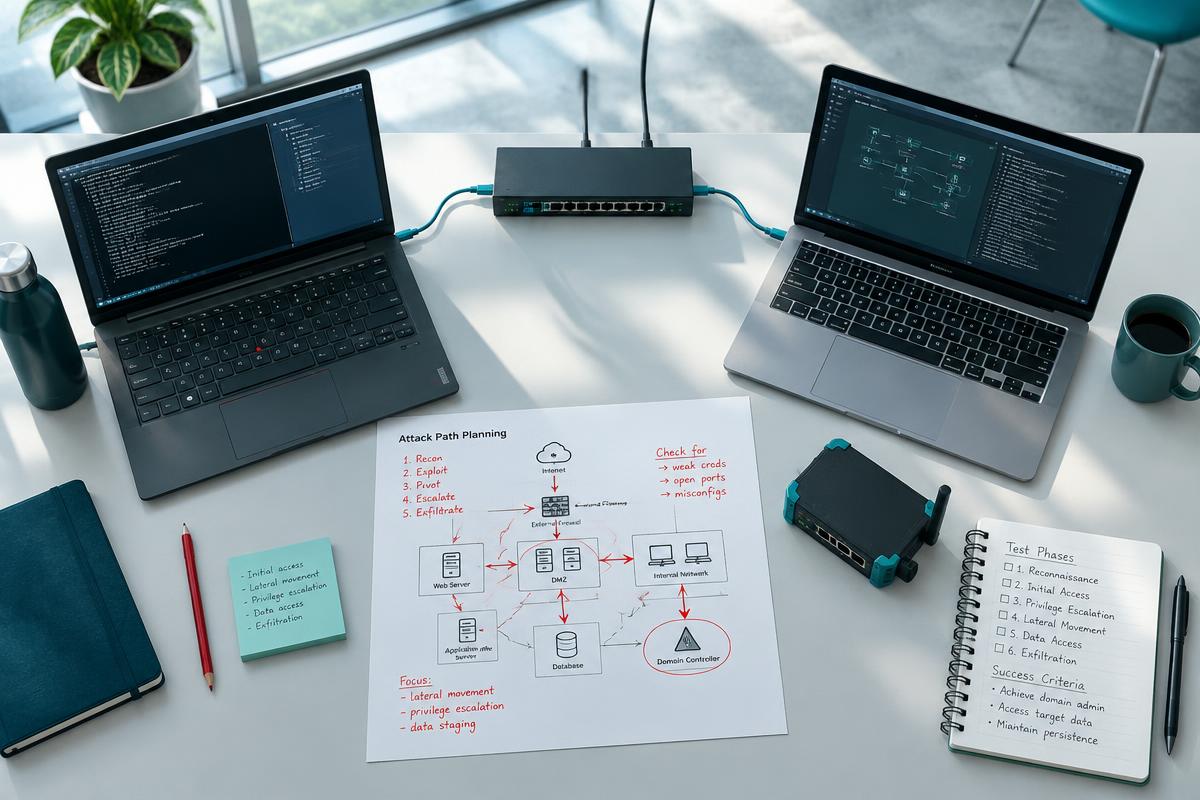
Red Teaming
Test whether the defenders can see you, not just whether a host is vulnerable.
View curriculum